More about stolen bitcoins
Submitted by brad on Wed, 2014-03-05 14:58Yesterday, I wrote about stolen bitcoins and the issues around a database of stolen coins. The issue is very complex, so today I will add some follow-up issues.
Topic:
Tags:


Brad Templeton is Chairman Emeritus of the EFF, Singularity University founding computing faculty, software architect and internet entrepreneur, robotic car strategist, futurist lecturer, photographer and Burning Man artist.
This is an "ideas" blog rather than a "cool thing I saw today" blog. Many of the items are not topical. If you like what you read, I recommend you also browse back in the archives, starting with the best of blog section. It also has various "topic" and "tag" sections (see menu on right) and some are sub blogs like Robocars, photography and Going Green. Try my home page for more info and contact data.
Yesterday, I wrote about stolen bitcoins and the issues around a database of stolen coins. The issue is very complex, so today I will add some follow-up issues.
Bitcoin has seen a lot of chaos in the last few months, including being banned in several countries, the fall of the Silk Road, and biggest of all, the collapse of Mt. Gox, which was for much of Bitcoin's early history, the largest (and only major) exchange between regular currencies and bitcoins. Most early "investors" in bitcoin bought there, and if they didn't move their coins out, they now greatly regret it.
I've been quite impressed by the ability of the bitcoin system to withstand these problems. Each has caused major "sell" days but it has bounced back each time. This is impressive because nothing underlies bitcoins other than the expectation that you will be able to use them into the future and that others will take them.
It is claimed (though doubted by some) that most of Mt.Gox's bitcoins -- 750,000 of them or over $400M -- were stolen in some way, either through thieves exploiting a bug or some other means. If true, this is one of the largest heists in history. There are several other stories of theft out there as well. Because bitcoin transactions can't be reversed, and there is no central organization to complain to, theft is a real issue for bitcoin. If you leave your bitcoin keys on your networked devices, and people get in, they can transfer all your coins away, and there is no recourse.
Or is there?
 If you sell something and are paid in stolen money, there is bad news for you, the recipient of the money. If this is discovered, the original owner gets the money back. You are out of luck for having received stolen property. You might even be suspected of being involved, but even if you are entirely innocent, you still lose.
All bitcoin transactions are public, but the identities of the parties are obscured. If your bitcoins are stolen, you can stand up and declare they were stolen. More than that, unless the thief wiped all your backups, you can 99.9% prove that you were, at least in the past, the owner of the allegedly stolen coins. Should society accept bitcoins as money or property, you would be able to file a police report on the theft, and identify the exact coin fragments stolen, and prove they were yours, once. We would even know "where" they are today, or see every time they are spent and know who they went to, or rather, know the random number address that owns them now in the bitcoin system. You still own them, under the law, but in the system they are at some other address.
That random address is not inherently linked to this un-owner, but as the coins are spent and re-spent, they will probably find their way to a non-anonymous party, like a retailer, from whom you could claim them back. Retailers, exchanges and other legitimate parties would not want this, they don't want to take stolen coins and lose their money. (Clever recipients generate a new address for every transaction, but others use publicly known addresses.)
It's possible, not even that difficult, to create a database of "tainted" coins. If such a database existed, people accepting coins could check if the source transaction coins are in that database. If there, they might reject the coins or even report the sender. I say "reject" because you normally don't know what coins you are getting until the transaction is published, and if the other party publishes it, the coins are now yours. You can refuse to do your end of the transaction (ie. not hand over the purchased goods) or even publish a transaction "refunding" the coins back to the sender. It's also possible to imagine that the miners could refuse to enter a transaction involving tainted coins into the blockchain. (For one thing, if the coins are stolen, they won't get their transaction fees.) However, as long as some miner comes along willing to enter it, it will be recorded, though other miners could refuse to accept that block as legit.
In my recent travels, I have often been asked what various government entities can and should do related to the regulation of robocars. Some of them want to consider how to protect public safety. Most of them, however, want to know what they can do to prepare their region for the arrival of these cars, and ideally to become one of the leading centres in the development of the vehicles. The car industry is about to be disrupted, and most of the old players may not make it through to the new world.
It was revealed earlier this month that NHTSA wishes to mandate vehicle to vehicle radios in all cars. I have written extensively on the issues around this and regular readers will know I am a skeptic of this plan. This is not to say that I don't think that V2V would not be useful for robocars and regular cars. Rather, I believe that its benefits are marginal when it comes to the real problems, and for the amount of money that must be spent, there are better ways to spend it. In addition, I think that similar technology can and will evolve organically, without a government mandate, or with a very minimal one. Indeed, I think that technology produced without a mandate or pre-set standards will actually be superior, cheaper and be deployed far more quickly than the proposed approach.
The new radio protocol, known as DSRC, is a point-to-point wifi style radio protocol for cars and roadside equipment. There are many applications. Some are "V2V" which means cars report what they are doing to other cars. This includes reporting one's position tracklog and speed, as well as events like hitting the brakes or flashing a turn signal. Cars can use this to track where other cars are, and warn of potential collisions, even with cars you can't see directly. Infrastructure can use it to measure traffic.
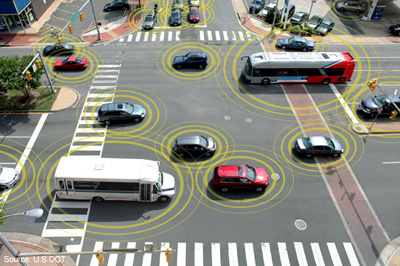 The second class of applications are "V2I" which means a car talks to the road. This can be used to know traffic light states and timings, get warnings of construction zones and hazards, implement tolling and congestion charging, and measure traffic.
This will be accomplished by installing a V2V module in every new car which includes the radio, a connection to car information and GPS data. This needs to be tamper-proof, sealed equipment and must have digital certificates to prove to other cars it is authentic and generated only by authorized equipment.
Robocars will of course use it. Any extra data is good, and the cost of integrating this into a robocar is comparatively small. The questions revolve around its use in ordinary cars. Robocars, however, can never rely on it. They must be be fully safe enough based on just their sensors, since you can't expect every car, child or deer to have a transponder, ever.
One issue of concern is the timeline for this technology, which will look something like this:
Because of the quadratic network effect, in 2030 when half of cars have the technology, only 25% of car interactions will be make use of it, since both cars must have it. (The number is, to be fair, somewhat higher as new cars drive more than old cars.)
The Robocars world tour continues. Monday I will speak on robocars at the UAE Government conference in Dubai, where I just landed. Then it's off to talk about them at a private event in Singapore, but I'll also visit teams there. If I have time, I will check out Masdar -- what was originally going to be the first all-robocar city -- while in the UAE.
Very long-time readers of this blog will remember a proposal I made 10 years ago that cruise ship inside cabins use HDTVs with the outside view. Now a cruise ship is launching with such a system, though bigger than I proposed.
A lot of sites, most notably search engines like Google, like to rewrite all the links on their pages. So search for this page and instead of http://ideas.4brad.com, the link Google gives you is http://www.google.com/url?sa=t&rct=j&q=&esrc=s&source=web&cd=1&cad=rja&ved=short-string&url=http%3A%2F%2Fideas.4brad.com%2F&ei=med-string&usg=huge-string&bvm=short-string or similar. (I have redacted the actual codes.)
I don't know who the person or people are who, under the name Satoshi Nakamoto, created the Bitcoin system. The creator(s) want to keep their privacy, and given the ideology behind Bitcoin, that's not too surprising.
There can only be 21 million bitcoins. It is commonly speculated that Satoshi did much of the early mining, and owns between 1 million and 1.5 million unspent bitcoins. Today, thanks in part to a speculative bubble, bitcoins are selling for $800, and have been north of $1,000. In other words, Satoshi has near a billion dollars worth of bitcoin. Many feel that this is not an unreasonable thing, that a great reward should go to Satoshi for creating such a useful system.
For Satoshi, the problem is that it's very difficult to spend more than a small portion of this block, possibly ever. Bitcoin addresses are generally anonymous, but all transactions are public. Things are a bit different for the first million bitcoins, which went only to the earliest adopters. People know those addresses, and the ones that remain unspent are commonly believed to be Satoshi's. If Satoshi starts spending them in any serious volume, it will be noticed and will be news.
Whether Bitcoin becomes a stable currency in the future or not, today few would deny it is not stable, and undergoing speculative bubbles. Some think that because nothing backs the value of bitcoins, it will never become stable, but others are optimistic. Regardless of that, today the value of a bitcoin is fragile. The news that "Satoshi is selling his bitcoins!" would trigger panic selling, and that's bad news in any bubble.
 If Satoshi could sell, it is hard to work out exactly when the time to sell would be. Bitcoin has several possible long term fates:
My personal prediction is #3 -- that several successor currencies will arise which fix issues with Bitcoin, with exchange possible for a while. However, just as bitcoins had their sudden rushes and bubbles, so will this exchange rate, and as momentum moves into this currency it could move very fast. Unlike exchanges that trade bitcoins for dollars, inter-cryptocurrency exchanges will be fast (though the settlement times of the currencies will slow things down.) It could be even worse if the word got out that "Satoshi is trading his coins for [Foo]Coin" as that could cause complete collapse of Bitcoin.
Perhaps he could move some coins through randomizing services that scramble the identity association, but moving the early coins to such a system would be seen as selling them.
Recently I learned from health.net, the insurer which did my individual plan, that they were canceling it. I'm one of those who lost his health plan with the switch to the ACA (Obamacare) plans, so I need to shop in the healthcare marketplace and will likely end up paying more.
What surprised me when I went to the marketplace was the math of the plans. For those who don't know, there are 4 main classes of plans (Bronze, Silver, Gold, Platinum) which are roughly the same for all insurers. There is also a 5th, "Catastrophic" plan available to under-30s and hardship cases, which is cheaper and covers even less than Bronze. Low income people get a great subsidized price in the marketplace, but people with decent incomes get no subsidy.
The 4 plans are designed so that for the average patient, they will end up paying 60% (Bronze), 70% (Silver), 80% (Gold) or 90% (Platinum) of health care costs, with the patient, on average, bearing the rest. All plans come with a "Maximum out of pocket" (MOOP) that is at most $6,350 for all plans but $4,000 (or less) for the Platinum.
Here's some analysis based on California prices and plans. The other states can vary a fair bit. Insurance is much cheaper in some regions, and there are plans that use moderately different formulae. In every state the MOOP is no more than $6,350 and the actuarial percentages are the same.
As you might expect, the Platinum costs a lot more than the Bronze. But at my age, in my early 50s, I was surprised how much more. I decided to plug in numbers for Blue Cross, which is actually slightly cheaper than many of the other plans. I actually have little information with which to compare the companies. This is quite odd -- my health insurance is going to be by biggest annual expenditure after my mortgage. More than my car -- but there's tons of information to help you choose a car. (Consumer Reports does have a comparison article on the major insurance companies before the ACA for their subscribers.)
The Platinum plan costs $350/month extra over Bronze, $4200/year. Almost as much as the MOOP. So I decided to build a spreadsheet that would show me what I would end up paying on each plan in total -- premiums plus my personal outlays. Here is the sheet for me in my early 50s:
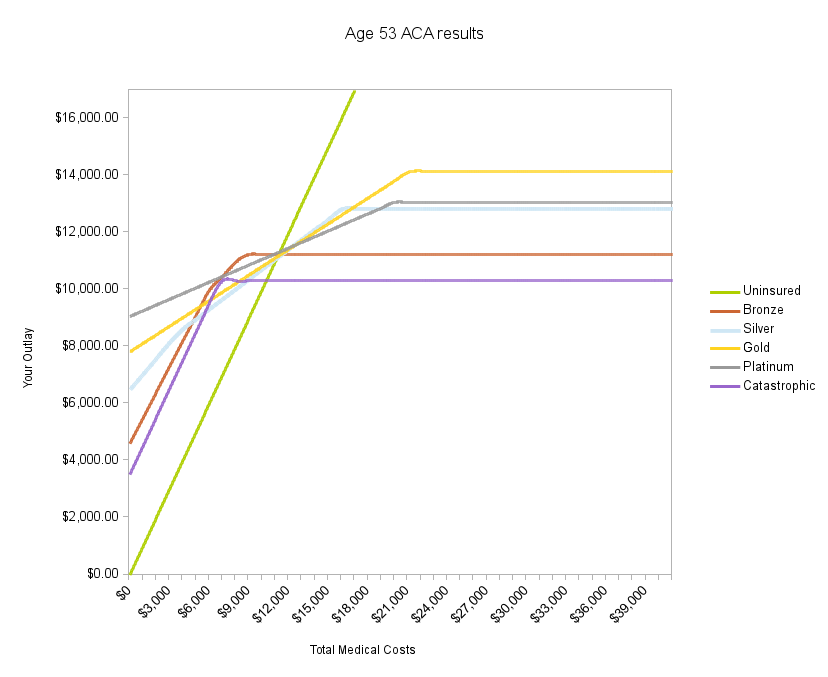
The X axis is how much your health care actually cost, ie. what your providers were paid. The Y axis is how much you had to pay. The green line is unity, with your payout equal to the cost, as might happen in theory if you were uninsured. In theory, because in reality uninsured people pay a "list price" that is several times the cost that insurance companies negotiate. Also in theory because those uninsured must pay a tax penalty.
All the plans go up at one rate until they first hit your deductibles (Bronze/Silver) and then at a slower rate until you hit your MOOP. After the MOOP they are a flat line almost no matter what your health spending does. The Silver plan is the most complex. It has a $250 drug deductible and a $2000 general deductible and the usual $6,350 MOOP. In reality, these slopes will not be smooth lines. For example, on the silver plan if you are mostly doing doctor visits and labs, you do copays, not the deductible. If you hit something else, like MRI scans or hospitalization, you pay out the full cost until you hit the deductible. So each person's slope will be different, but these slopes are meant to represent an estimate for average patients.
The surprising thing about this chart is that the Bronze plan is pretty clearly superior. Only for a small region of costs does your outlay exceed the other plans, and never by much. However, in the most likely region for most people (modest health care) or the danger zone (lots of health care) it is quite a bit cheaper. The catastrophic plan, if you can get your hands on it over 30, is even better. It almost never does worse than the other plans.
I will note that the zone where Bronze is not the winner is around the $8,400 average cost of health care in the USA. However, what I really want to learn is the median cost, a statistic that is not readily available, or even better the median cost or distribution of costs at each age cohort. The actuaries obviously know this, and I would like pointers to a source.
Premiums are tax deductible for the self-employed, as are large medical expenses for all, but the outlays above premiums can also come from a Health Savings Account (HSA) which is a special IRA-like instrument. You put in up to around $3K each year tax-free, and can pay the costs above from it. (You also don't pay tax on appreciation of the account, and can draw out the money post-retirement at a decent rate.) If you are self-employed, depending on your tax bracket, this can seriously alter the chart and push you to a more expensive plan, because the premium money comes from pre-tax dollars and the health expenses don't, unless they are more than 10% of your total income.
The chart suggests the Bronze plan is the clear winner unless you know you will be in the $6K to $10K zone where it's a modest loser. It seems to beat the Platinum all the time (at least in this simplified model) but might have minor competition from the Silver. The Gold is essentially always worse than the Silver.
If we move to age 60, now the win for Bronze is very clear. At age 60, the $5500 extra premium for Platinum almost exceeds the MOOP on the Bronze -- the Bronze will always be cheaper. This makes no sense, and seems to be a result of the fact that the MOOP remains the same no matter how old you are (and is also the same for B/S/G/Cat.) Perhaps varying deductibles and the MOOP over time would have made more variety.

Here the Gold is clearly a loser to the Silver if you were thinking about it. Nobody in this age group should buy the Gold plan but I doubt the sites will say that. Platinum is almost as clearly a loss.
With the choice for the older person so obvious, this opens up another question, namely one of psychology. The rational thing to do is to buy the Bronze plan. But with its $5,000 deductible, you will find yourself paying out of pocket for almost all your health care except in years you need major treatments and hospitalizations.
I'm working on a new long article about advice to governments on how they should react to and encourage the development of robocars.
An interesting plan announced today has something I had not thought of: Michigan is funding the development of a fake downtown to act as a test track for robocar development. The 32 acre site will be at the University of Michigan, and is expected to open soon -- in time for the September ITS World Congress.
The Olympics are coming up, and I have a request for you, NBC Sports. It's the 21st century, and media technologies have changed a lot. It's not just the old TV of the 1900s.
An article in the LA Times suggests an idea I've seen frequently -- use electric car batteries to meet peak power demand on the grid. After all, you have a car, and it's plugged in, and it has a big battery, so instead of just charging it, have it send juice back to the grid when it most needs it.
With last week's commercial release of the Navia, I thought I would release a new essay on the challenges of driving robocars at different speeds.
As the Navia shows, you can be safe if you're slow. And several car company "traffic jam assist" products say the same thing. On the other end, we see demos taking place at highway speeds. But what about the middle range -- decent speeds on urban streets?
A significant milestone was announced this week. Induct has moved their "Navia" vehicle into commercial production, and is now taking orders, though at $250,000 you may not grab your wallet.
This is the first commercial robocar. Their page of videos will let you see it in operation in European pedestrian zones. It operates unmanned, can be summoned and picks up passengers. It is limited to a route and stops programmed into it.
CES has become a big show for announcing car technology. I'm not there this year due to other engagements, but here's some of what has been in the news.
A big story this Christmas was a huge surge in the use of rush shipping in the last 2 days before Christmas. Huge numbers of people signed up for Amazon Prime, and other merchants started discounting 2 day and overnight shipping to get those last minute sales. In turn, a lot of stuff didn't get delivered on time, making angry customers and offers of apology discounts from merchants. This was characterized as a "first world problem" by many outside the game, of course.
One of the silly ideas I see often is the solar powered car. In 2011, I wrote an article about the solar powered robocar which explained some of the reasons why the idea is anti-green, and how robocars might help.
I was interested to see a concept from Ford for a solar charging station for a robocar which goes further than my idea.
In part 1 I outlined the many problems caused by wifi login pages that hijack your browser ("captive portals") and how to improve things.
Today I want to discuss the sad state of having security in WIFI in most of the setups used today.
Almost all open WIFI networks are simply "in the clear." That means, however you got on, your traffic is readable by anybody, and can be interfered with as well, since random users near you can inject fake packets or pretend to be the access point. Any security you have on such a network depends on securing your outdoing connections. The most secure way to do this is to have a VPN (virtual private network) and many corporations run these and insist their employees use them. VPNs do several things:
VPNs have downsides. They are hard to set up. If you are not using a corporate VPN, and want a decent one, you typically have to pay a 3rd party provider at least $50/year. If your VPN router is not in the same geographic region as you are, all your traffic is sent to somewhere remote first, adding latency and in some cases reducing bandwidth. Doing voice or video calls over a VPN can be quite impractical -- some VPNs are all TCP without the UDP needed for that, and extra latency is always a killer. Also, there is the risk your VPN provider could be snooping on you -- it actually can make it much easier to snoop on you (by tapping the outbound pipe of your VPN provider) than to follow you everywhere to tap where you are.
If you don't have a VPN, you want to try to use encrypted protocols for all you do. At a minimum, if you use POP/IMAP E-mail, it should be configured to only get and receive mail over TLS encrypted channels. In fact, my own IMAP server doesn't even accept connections in the clear to make sure nobody is tempted to use one. For your web traffic, use sites in https mode as much as possible, and use EFF's plugin https everywhere to make your browser switch to https wherever it can.
This year, we stayed with Kathryn's family for the holidays, so I attended dinner in my own mother's home via Skype. Once again, the technology was frustrating. And it need not be.
There were many things that can be better. For those of us who Skype regularly, we don't understand that there is still hassle for those not used to it. Setting up a good videoconferencing setup is still work. As I have found is always the case in a group-to-solos videoconference, the group folks do not care nearly as much about the conference as the remote solos, so a fundamental rule of design here is that if the remotes can do something, they should be the ones doing it, since they care the most. If there is to be UI, leave the UI to the remotes (who are sitting at computers and care) and not to the meeting room locals. Many systems get this exactly backwards -- they imagine the meeting room is the "master" and thus has the complex UI.
In this family setting, however, the clearest problem for me is that no camera can show the whole room. It's like sitting at the table unable to move your head, with blinders on. You can't really be part of the group. You also have to be away from the table so everybody there can see you, since screens are only visible over a limited viewing angle.
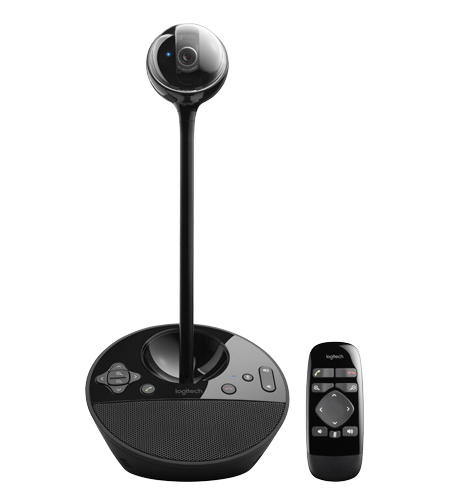
One clear answer to this is the pan/tilt camera, which is to say a webcam with servo motors that allow it to look around. This technology is very cheap -- you'll find pan/tilt IP security cameras online for $30 or less, and there are even some low priced Chinese made pan/tilt webcams out there -- I just picked another up for $20. I also have the Logitech Orbit AF. This was once a top of the line HD webcam, and still is very good, but Logitech no longer makes it. Logitech also makes the BCC950 -- a $200 conference room pan/tilt webcam which has extremely good HD quality and a built-in hardware compressor for 1080p video that is superb with Skype. We have one of these, and it advertises "remote control" but in fact all that means is there is an infrared remote the people in the room can use to steer the camera. In our meetings, nobody ever uses this remote for the reason I specify above -- the people in the room aren't the motivated ones.
This is compounded by the fact that the old method -- audio conference speakerphones -- have a reasonably well understood UI. Dial the conference bridge, enter a code, and let the remotes handle their own calling in. Anything more complex than that gets pushback -- no matter how much better it is.
I've made some updates to my Better to Give than Receive Gift Guide for Christmas Eve.
In particular, to help understand the philosophy of the guide (which forbids cash and gift cards, among other things) I propose you imagine the world where you, and all those who you would give gifts to are billionaires. The reality is the money amount of gifts between adults is normally a blip in the annual budget, so reality is not too far from this hypothetical.